
A Windows RDP for remote teams needs more than a working login when employees connect from different time zones, networks, and schedules.
Remote teams often assume any Windows RDP will work as soon as everyone gets the login details. The problems usually show up later, when one employee is handing over work while another is logging in, several users connect at once, or someone in another region feels extra lag. Connection drops, session conflicts, and inconsistent speed can turn a simple remote setup into a daily headache.
Web Pundits’ RDP guidance focuses on practical access and server configuration, not just getting someone connected. For a solid remote desktop setup for distributed teams, user access, server location, session policies, and security all need to be planned together, not bolted on afterward.
If you’re planning to buy USA RDP, server location should match where most of your team actually connects from.
Key Takeaways
- Overlapping time zones can create RDP session conflicts during handovers.
- Separate accounts make access, permissions, troubleshooting, and offboarding far easier.
- Server location affects latency and how responsive each session feels.
- Network Level Authentication (NLA) adds a key security layer to RDP.
- MFA adds another layer of protection for remote access.
- Session limits and idle timeouts stop forgotten connections from staying open.
- Always test with real users, real locations, and overlapping work hours before you roll it out.
Why Do Time Zones Create Unique Windows RDP Problems?
The issue isn’t that employees work different hours. It’s that those hours overlap in ways nobody planned for when the server was set up.
A team member in London might be wrapping up just as someone in New York logs in. A US employee may reconnect at the same moment a colleague in Europe is handing off a project. When those sessions land together, Windows RDP for remote teams has to handle the extra users, apps, and traffic without tripping over itself.
Simultaneous logins can expose configuration gaps
How many people a Windows Server RDP environment can support at once depends on the Windows edition, the Remote Desktop Services setup, licensing, configured connection limits, and available server resources.
This matters most during handovers. Picture one employee finishing their shift but leaving the session disconnected instead of closed. A colleague logs in to pick up the work. If this happens across the team throughout the day, several disconnected sessions can remain active until they are ended or timed out, using server resources in the meantime. Windows does let you restrict a user to a single session, which helps avoid exactly this.
Different working hours create bandwidth peaks
Time zones shift when your RDP environment hits its busiest point. A quiet stretch can suddenly become a peak window the moment two or three regions are online together, pushing up:
- Active RDP sessions
- Application usage
- File transfers
- Browser activity
- Database access
- Network traffic
- CPU and RAM demand
The goal isn’t to stop people working at the same time. It’s to plan the environment around how many will realistically be connected together.
How Should You Configure RDP Access for a Remote Team?
A solid remote desktop setup for distributed teams starts with individual accounts and clear permissions.
Give every employee a separate account
Don’t run the whole team through one shared username and password. Separate accounts make it simple to see who’s connected, assign the right permissions, remove access the moment someone leaves, and investigate anything unusual. For a growing team, grouping users makes permission management far less tedious than configuring everyone one by one.
Give users only the access they need
Not everyone should have admin rights. A person who simply opens a business application should also not be able to install software or modify security settings. A practical structure looks like:
- Standard employees – app access only
- Team leads – slightly broader access, no system changes
- Application admins – manage specific apps
- Server admins – full control, kept to a small group
Fewer high-privilege accounts means fewer places where something can go wrong.
Set sensible session limits
Session policies matter most when a team spans time zones. Windows lets you cap simultaneous connections and restrict users to one session each, plus set rules for active, idle, and disconnected sessions. The aim isn’t to kick people off aggressively; it’s to stop forgotten sessions sitting open indefinitely while still giving people enough time to finish real work.
How Does Server Location Affect RDP Performance?
An RDP session depends on constant back-and-forth between the employee’s device and the server, so distance plays a real role. Geographic distance can add latency, though routing, congestion, packet loss, ISP quality, and the user’s own connection all factor in too.
Match the server region to your team
If most of your team works from the US with a smaller group in Europe, a US-based server is a sensible starting point since it sits closer to the majority. Still test with the European users included. If the team is split roughly evenly across continents, the decision gets harder, so weigh:
| Factor | Why it matters |
| Where most users sit | Drives the baseline latency for the group |
| Where apps and data live | Server should sit close to what it’s serving |
| Where customers are | Relevant if the server also faces customers |
| Expected latency per region | Sets expectations before go-live |
| Compliance or data rules | Some regions require local hosting |
| Users per region | A 90/10 split behaves differently to a 50/50 one |
Don’t pick a location just because the country name sounds right for your business.
According to Web Pundits, choosing an RDP server location should take into account where your users connect from and how they use the remote environment. A location that works well for one region may not deliver the same experience for a distributed team, which is why testing from multiple locations matters.
Test from multiple locations
Before rolling RDP out to the whole team, test it from real locations people actually work from. Check how fast apps open, how smooth the desktop feels, and whether keyboard and mouse input lags. Test during overlapping hours too. A connection that feels great for one person at 8 am can feel very different once several people are active on it at once.
How Should You Secure a Multi-User RDP Environment?
With several employees sharing one server environment, Windows RDP for remote teams needs to be treated as a security boundary, not just a convenience.
Enable Network Level Authentication
NLA requires authentication before a full Remote Desktop session even opens. It’s worth keeping on wherever possible. Turning it off just to support one old client shouldn’t be the default move.
Add multifactor authentication
A password is only one factor. MFA asks for extra verification, so a leaked password alone isn’t enough to get in. For a distributed team connecting from different networks and devices, this matters even more.
Restrict unnecessary network exposure
Don’t open remote access any wider than it needs to be. Depending on your setup, consider:
- VPN access
- Remote Desktop Gateway
- Firewall restrictions
- Approved network ranges
- Conditional access controls
- IP allowlisting where practical
IP allowlisting is great for personnel on stable, known networks but needs more maintenance for those bouncing between home, office, and mobile connections.
If you’re comparing where to buy RDP online, weigh the security and access setup alongside basic availability, not as an afterthought.
Configure session timeouts
An employee might close their laptop without signing out properly, leaving a session disconnected or idle. Windows lets you set limits for active, idle, and disconnected sessions. Pick limits that fit how your team actually works. Too short, and you interrupt real work. Too loose, and sessions stay open far longer than intended.
What Should You Check Before Deploying RDP for a Distributed Team?
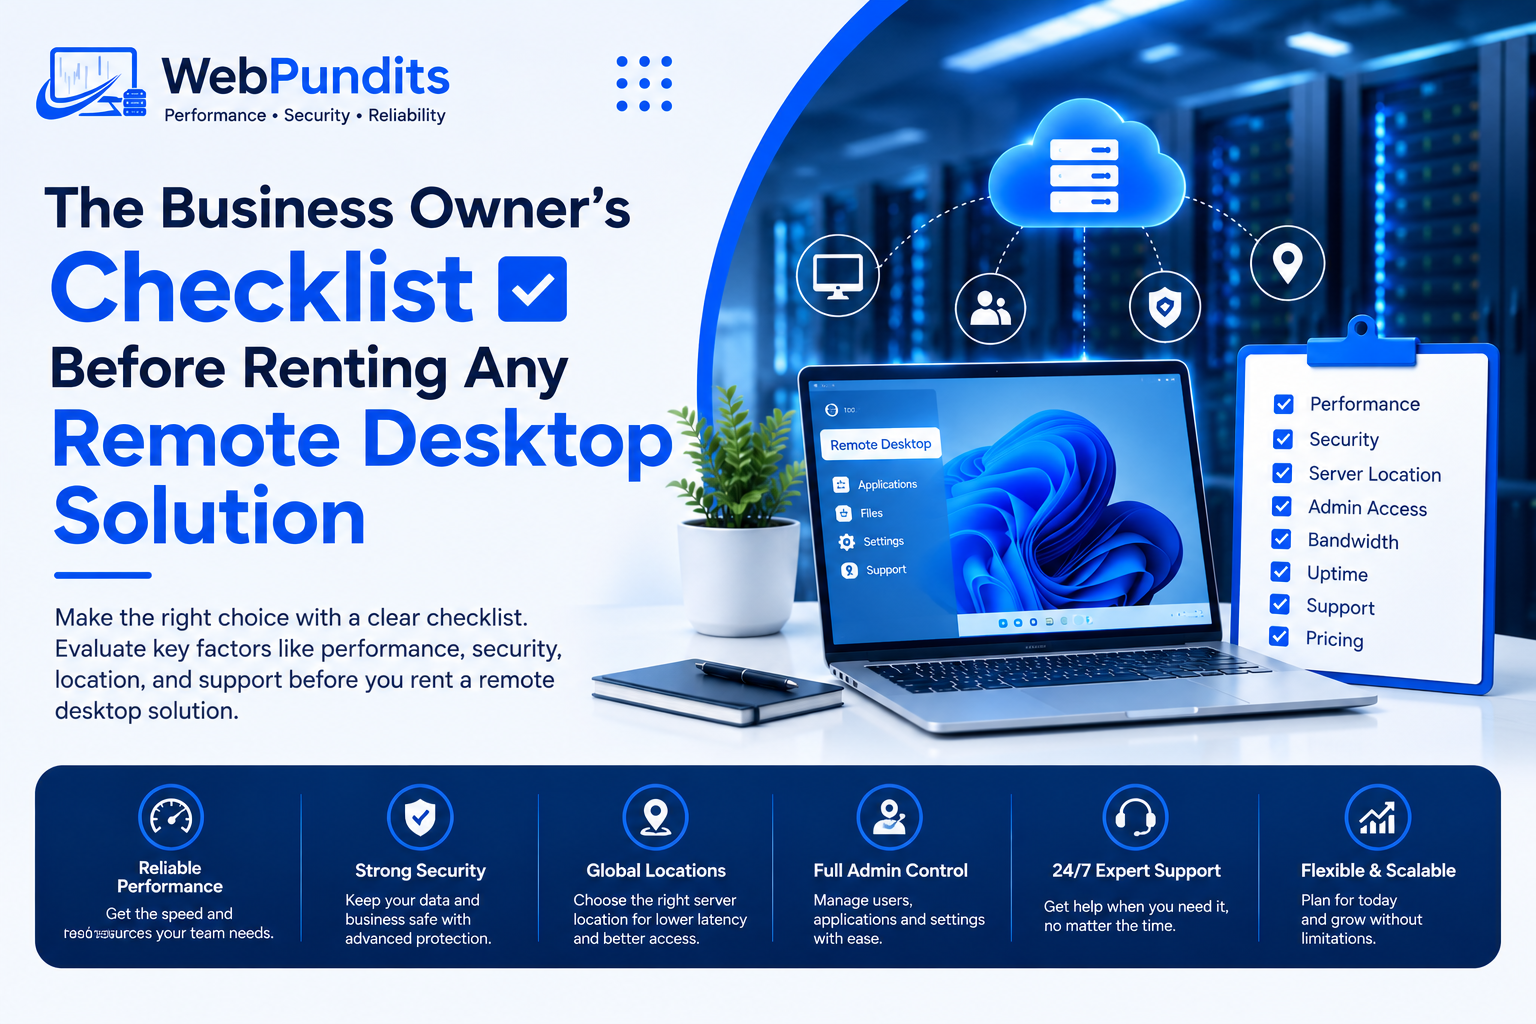
Before deploying RDP to a distributed team, check user access, session limits, network performance, and security settings. A quick review of these areas can help catch configuration issues before they affect everyday work.
User and permissions
- Individual account for every employee
- Groups used where it simplifies permissions
- Admin access kept limited
- Clear list of who’s allowed to connect
- A defined handover process for shift changes
- A process for removing access when someone leaves
Sessions
- Expected number of simultaneous users mapped out
- Server and RDS configuration reviewed
- Connection limits checked
- Clear rule for handling disconnected sessions
- Idle-session limits set
- Tested what happens at the max connection count
Network
- Employee locations mapped
- Server location chosen by user distribution, not guesswork
- Latency tested from multiple regions
- Checked for packet loss and instability
- Tested during overlapping work hours
- Gateway or VPN access considered where needed
Security
- NLA enabled
- Strong, unique passwords enforced
- MFA turned on where supported
- Unnecessary network exposure restricted
- Firewall rules reviewed
- Access reviewed regularly, removed promptly on exit
Performance
Don’t test with one person and assume it’s ready for everyone. Run a real test: several users connected, the actual apps they use open, real files moving, normal browser tasks running, and collaboration tools included if they’re part of the day-to-day. Most importantly, test during a realistic handover window when people from different time zones are likely to overlap. That’s the only way to see how the environment behaves under real load.
Need a More Reliable Setup for Your Remote Team?
Managing a team across time zones gets hard fast when RDP sessions are slow, dropping, or poorly configured. A well-set-up Windows RDP environment gives your team a consistent way to reach applications, files, and work resources, without everyone needing to be online at once.
Webpundits can help you explore RDP options for remote access and build an environment around how your team actually works. Whether you’re starting a new distributed workflow or fixing an existing one, a properly planned remote desktop setup for distributed teams can make everyday remote work far more predictable.
[Get Started With Windows RDP]
FAQs
Can Windows RDP support multiple remote team members?
Yes. A properly configured Windows Server Remote Desktop Services environment can support multiple sessions. How much depends on the Windows configuration, RDS setup, licensing, connection limits, and available server resources.
Should every remote employee have a separate RDP account?
Yes. Separate accounts make it far easier to manage permissions, see who’s active, investigate issues, and remove access when someone leaves.
Does RDP server location affect remote team performance?
It can. Distance contributes to latency, though routing, congestion, packet loss, and local network conditions matter too. Testing from real user locations is the most reliable way to check it.
How can I stop employees leaving RDP sessions open?
Set clear handover steps and configure session policies. Windows RDS supports limits for idle and active sessions, plus rules for handling disconnected ones.
Is MFA necessary for a multi-user RDP environment?
Strongly recommended wherever it’s supported. It adds a second identity check, which cuts the risk of unauthorized access if a password leaks.